Last updated: October 2026
Key takeaways
- The DPDP Act applies to AI training data whenever a dataset holds digital personal data about an identifiable person. That includes voices, faces, names in free text and speaker metadata.
- The DPDP Rules, 2025 start in three phases. Board rules applied on notification. Consent manager registration follows after 12 months (around 13 November 2026). Most duties follow after 18 months (around 13 May 2027).
- Consent must be free, specific, informed, unconditional and unambiguous. AI training should appear as its own named purpose in an itemized, plain-language notice.
- The buyer is usually the Data Fiduciary and stays legally responsible. The collection or annotation vendor acts as a Data Processor under a valid contract and must support security, breach reporting and erasure.
- Penalties reach up to ₹250 crore for security failures. Check consent evidence before any file enters a training pipeline, not after.
The DPDP Act AI training data question has moved from legal theory to procurement checklists. India’s Digital Personal Data Protection Act, 2023 and the DPDP Rules, 2025 now govern how teams collect, label, store and delete personal data for model training. Most core duties start in May 2027, and datasets bought this quarter will still be in use then.
This guide is for AI teams that buy speech, video or text data, and for the vendors that collect and annotate it. It covers scope, the verified rules timeline, consent and processor duties. It ends with an 8‑point buyer checklist for your next vendor review. If you track India data protection and AI policy, the timeline section is the one to bookmark.
This article is general information, not legal advice. Check the Act, the Rules and your own counsel before you act on it.
Sourcing Indian data for a 2027 model? Ask us for our consent & data-handling pack before you sign a vendor.
What does the DPDP Act cover for AI training data?
The DPDP Act covers the processing of digital personal data in India. Personal data means any data about an individual who is identifiable by or in relation to that data. Processing includes collection, recording, structuring, storage, use, sharing and erasure. That maps directly onto collection, annotation and model training. In short: if a person can be identified, the Act applies.
Section 3 of the Act applies to personal data collected in digital form in India, or collected on paper and digitized later. It also reaches processing outside India when that processing is connected with offering goods or services to people in India [1].
Two exclusions matter for AI teams. The Act does not apply to data processed for purely personal or domestic purposes. It also does not apply to personal data made public by the person it relates to, or by someone legally required to publish it. We cover that second exclusion below, because it is often misread as a scraping license.
Four roles to map before any data moves
Every obligation in the Act attaches to a role. Map these on day one of a project, in writing.
| Role | Meaning in the Act | Typical party in an AI data project |
|---|---|---|
| Data Principal | The individual the data relates to. For a child, it includes the parent or lawful guardian. | Speakers, camera wearers, bystanders, annotators |
| Data Fiduciary | Decides the purpose and means of processing, alone or with others. | The AI company commissioning or buying the dataset |
| Data Processor | Processes personal data on behalf of a Data Fiduciary. | Collection, transcription and annotation vendors |
| Consent Manager | Registered with the Board. Lets a person give, manage, review and withdraw consent on one platform. | An optional consent platform chosen by the individual |
Roles follow decisions, not job titles. A vendor can be your processor for the dataset and also a fiduciary for its own participant onboarding and payment records. Agree that split before kickoff.
When do the DPDP Rules 2025 take effect?
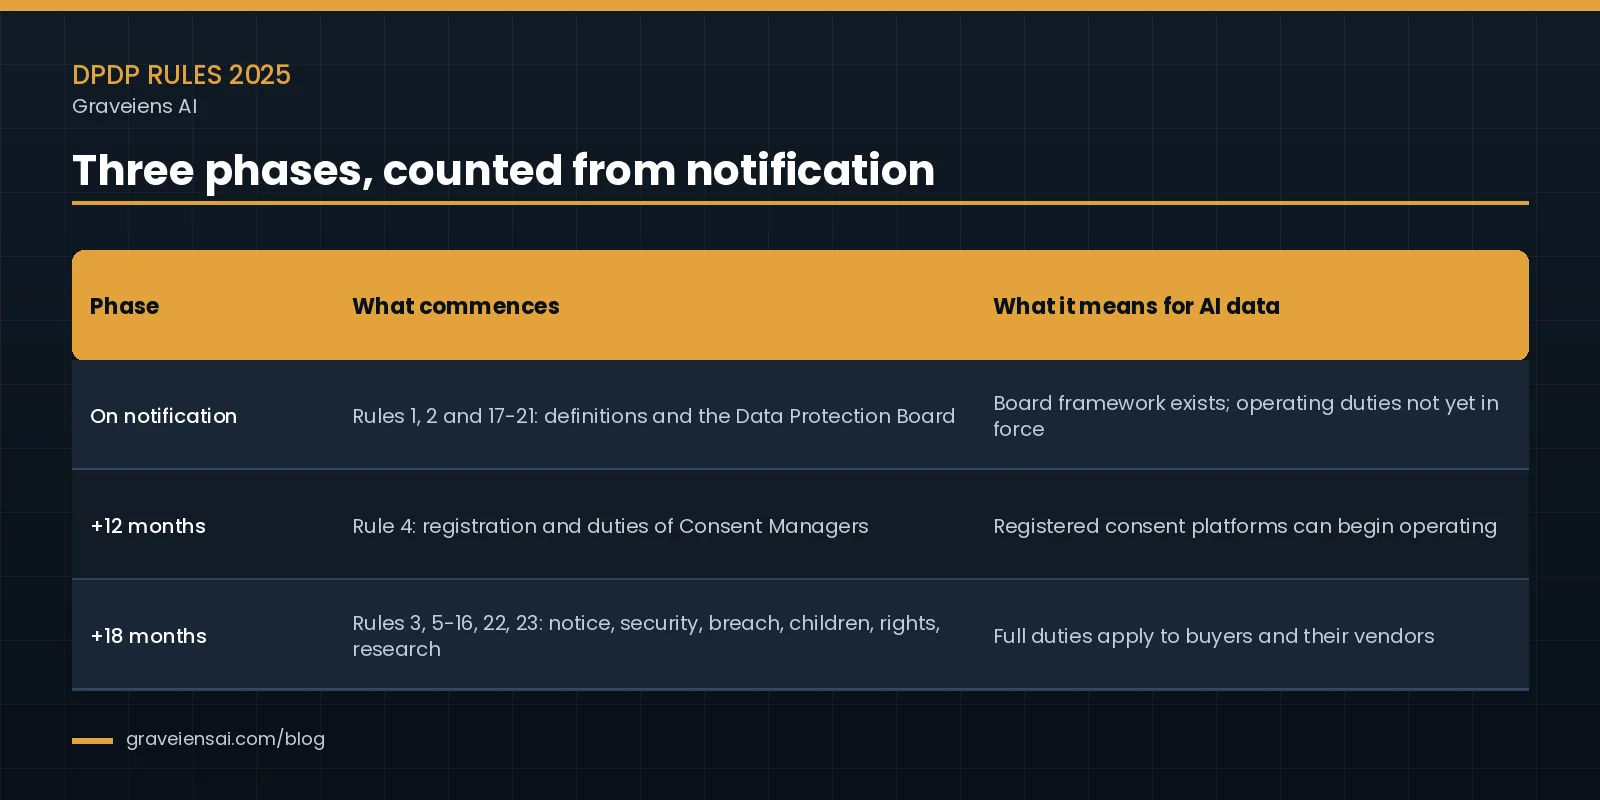
The DPDP Rules, 2025 were published in the Gazette as G.S.R. 846(E), dated 13 November 2025, and announced by the government on 14 November 2025. They commence in three phases. Board rules applied at once. Consent manager registration starts one year later. Notice, security, breach, children’s data and rights duties start eighteen months later, around 13 May 2027.
Rule 1 of the Rules sets the phases [2]. The government’s own summary describes “an eighteen-month period for phased compliance” [3]. Here is what each phase means for AI data work.
| Phase | Rules that commence | Approximate date | What it means for AI data |
|---|---|---|---|
| On notification | Rules 1, 2 and 17 to 21: definitions and the Data Protection Board | 13 November 2025 | Board framework exists; operating duties not yet in force |
| +12 months | Rule 4: registration and obligations of Consent Managers | Around 13 November 2026 | Registered consent platforms can begin operating |
| +18 months | Rules 3, 5 to 16, 22 and 23: notice, security, breach, retention, children, Significant Data Fiduciaries, rights, transfers, research standards | Around 13 May 2027 | Full duties for buyers and their vendors |
Some advisers count each date one day later, from the 14 November announcement. Confirm exact dates with counsel before you plan around them.
Has the 18-month timeline been shortened?
Not as of mid-October 2026. In January 2026, Business Standard reported a MeitY proposal to cut the window to 12 months for Significant Data Fiduciaries [4]. Some provisions would also start sooner. We found no Gazette notification making that change as of this update.
One small change did land. On 5 October 2026, MeitY issued the DPDP (Removal of Difficulties) Order, 2026, S.O. 5458(E), under Section 43 of the Act. It adds the word “of” in Section 9(1) and changes “audit” to “data audit” in Section 10(2)©(ii). Law firm reviews describe both edits as editorial. The order moves no deadline.
Our advice: plan to May 2027, but build your consent and breach processes as if the date could move earlier.
What counts as personal data in AI training datasets?
Personal data in training datasets is any data about an individual who can be identified from it, directly or in combination. In AI work, that includes voice recordings, faces in video, names and phone numbers in transcripts, speaker metadata such as age band and district, and annotator IDs. Removing names alone rarely makes a dataset non-identifiable.
Here is where personal data hides, by data type.
- Speech. A voice recording is data about the speaker. The spoken content may name other people. Metadata such as gender, age band, district and dialect narrows identity further. Our guide to Indic speech data collection covers how these fields are specified.
- Egocentric and other video. Faces, hands with jewelry or tattoos, number plates, screens, documents, house numbers and bystanders who never signed anything. See what to ask an egocentric data collection vendor about bystanders.
- Text and chat logs. Names, phone numbers, addresses and account numbers inside free text. Code-mixed Indic text is harder to redact automatically than English.
- Workforce data. Annotator IDs, productivity logs and payment details. Annotators are Data Principals too.
Is publicly available data exempt?
Only in part. Section 3©(ii) excludes personal data made public by the Data Principal herself, or by someone legally required to publish it [1]. The Act’s own example is a person who blogs her views on social media.
The exemption turns on who made the data public. A scraped corpus mixes self-published posts with reposts, leaks, aggregator listings and screenshots that the person never published. Law firm commentary in 2026 notes that large-scale commercial reuse for AI training remains unsettled. Document provenance per source, and do not assume a scrape sits outside the Act.
Does the research exemption cover model training?
Rarely for commercial products. Section 17(2)(b) says the Act does not apply to processing necessary for research, archiving or statistical purposes. Two conditions apply. The data must not be used to take any decision specific to a Data Principal. The processing must follow prescribed standards [1].
Rule 16 and the Second Schedule set those standards [2]. Processing must be lawful and limited to necessary data. It must aim for accuracy, keep data only as long as needed, apply security safeguards and have clear accountability. Rule 16 sits in the 18-month phase. A model that later drives decisions about individuals, such as credit scoring or personalized offers, is a weak fit. Treat the exemption as narrow and take advice before relying on it.
What about anonymized data?
The Act does not define anonymization. Data that is truly not about an identifiable person falls outside the definition of personal data. In practice, voices and faces are hard to make non-identifiable, so most raw speech and video datasets stay in scope.
What consent does the DPDP Act require for AI training data?
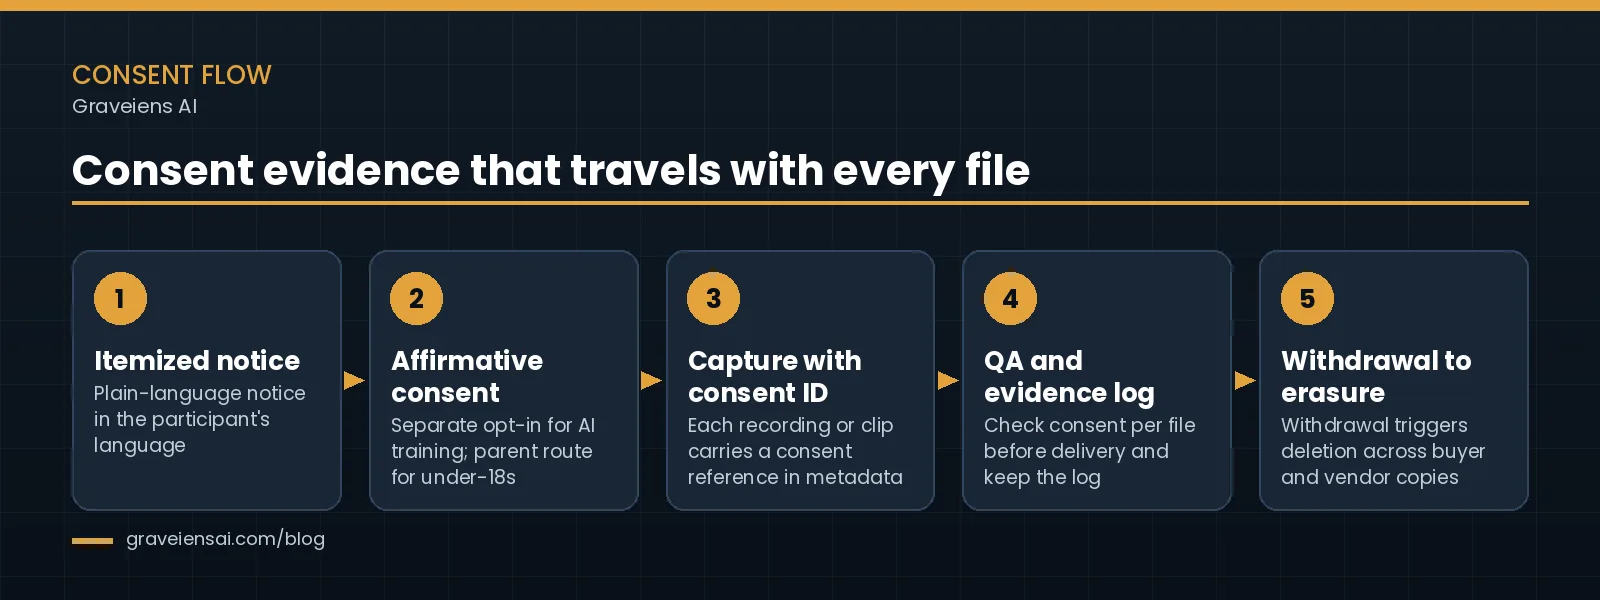
Consent must be free, specific, informed, unconditional and unambiguous, given by a clear affirmative action. It covers only the data needed for the specified purpose. It must follow an itemized, plain-language notice, offered in English or any Eighth Schedule language. Withdrawal must be as easy as giving consent, and the fiduciary must prove it all.
Those words come from Sections 5 and 6 of the Act [1]. The DPDP Rules 2025 consent notice standard sits in Rule 3 [2]. The notice must stand on its own and itemize the personal data. It must state the specified purpose and the uses it enables. It must also link to ways to withdraw consent, exercise rights and complain to the Board.
For AI data projects, four consequences follow.
- Name AI training as its own purpose. Consent given for a service does not cover model training. The Act’s telemedicine example shows consent shrinking to what the stated purpose needs.
- Offer the notice in the participant’s language. Sections 5(3) and 6(3) require the option of English or any language in the Eighth Schedule to the Constitution. For Indic speech collection, that usually means the language being recorded.
- Make withdrawal real. Under Section 6(6), the fiduciary must stop processing within a reasonable time and make its processors stop too. Decide early which artefacts get deleted: raw files, transcripts, labels and derived subsets.
- Keep proof. Section 6(10) puts the burden on the fiduciary to prove that notice was given and consent was obtained.
Consent is not the only lawful ground. Section 7 lists “certain legitimate uses”, such as legal obligations, medical emergencies and employment. There is no general “legitimate interests” ground of the GDPR kind. For commissioned data collection, consent is usually the practical basis. For voice projects, ask us for our speaker consent template, which is built around these rules.
Consent manager under the DPDP Act
A Data Principal may give, manage, review or withdraw consent through a Consent Manager registered with the Board (Section 6(7) to 6(9)). Rule 4 on registration commences one year after the Rules were published, around 13 November 2026 [2].
The First Schedule sets the bar. A Consent Manager must be a company incorporated in India with a net worth of at least ₹2 crore. It must not be able to read the personal data it helps share. It must keep consent records for at least seven years and avoid conflicts of interest with Data Fiduciaries. For buyers, the practical step is simple. Make sure your consent records can accept and honor signals from a registered platform if a participant uses one.
Children and guardians
A child is anyone under 18 (Section 2(f)). Before processing a child’s data, the fiduciary must obtain verifiable consent from a parent (Section 9(1)). Rule 10 requires due diligence that the person consenting is an identifiable adult. The check can use reliable identity and age details already held, or details the person provides [2]. It can also use a virtual token from an authorized entity, such as a DigiLocker service.
Section 9 also bars processing likely to harm a child’s well-being, and tracking, behavioral monitoring or targeted advertising directed at children. Persons with disability who have a lawful guardian need the guardian’s verifiable consent under Rule 11. For speech or household video projects, choose one path per project: exclude minors, blur them, or run a verified parental consent workflow.
What must a DPDP compliant data annotation vendor do?
The Act places legal duties on the Data Fiduciary, who stays responsible for everything its Data Processor does. A DPDP compliant data annotation vendor works only under a valid contract and on the buyer’s instructions. It applies the Rule 6 security safeguards, reports breaches fast enough for the 72-hour Board report, and stops processing and erases data when told.
The vendor duties come mostly through the fiduciary. Here is the chain, clause by clause.
- Responsibility stays with the buyer. Section 8(1) makes the fiduciary responsible for processing done on its behalf, whatever the contract says.
- A valid contract is mandatory. Section 8(2) allows a processor to be engaged only under a valid contract.
- Security safeguards cover the vendor. Rule 6 sets minimum measures [2]. They include encryption, masking or virtual tokens, access control, logging and monitoring, and backups. Logs and related personal data must be kept for one year to investigate incidents, unless another law says otherwise. The fiduciary-processor contract must include security terms.
- Breach reporting runs on two clocks. Under Rule 7, the fiduciary must tell each affected person and the Board without delay. A detailed Board report is due within 72 hours, unless the Board allows longer. Your vendor’s alert clause has to be much shorter.
- Withdrawal and erasure reach the vendor. Sections 6(6) and 8(7)(b) require the fiduciary to make its processors stop processing and erase data shared with them.
- Know your sub-processors. Under Section 11(1)(b), a person can ask the fiduciary to name every fiduciary and processor their data was shared with. Keep a current list.
One clause helps Indian vendors with overseas clients. Section 17(1)(d) exempts much of the Act for some offshore work. It applies when an India-based entity processes data of people outside India under a contract with a foreign party. Section 8(5) security safeguards and Section 8(1) responsibility still apply [1].
Who does what: buyer and vendor
| Obligation | Buyer (Data Fiduciary) | Vendor (Data Processor) |
|---|---|---|
| Notice and consent | Owns notice wording and purposes; must prove consent | Runs the notice and capture flow as instructed; keeps evidence |
| Security safeguards | Legally responsible, including for vendor processing | Encryption or masking, access control, logs, as contracted |
| Breach | Informs the Board and affected people; files the 72-hour report | Alerts the buyer at once with known facts |
| Withdrawal and erasure | Stops processing; directs erasure | Stops processing; deletes copies; confirms in writing |
| Rights requests | Answers access, correction and erasure requests | Finds records by consent ID; supports the response |
Penalties under the DPDP Act
The Schedule to the Act sets maximum penalties [1]. A failure to take reasonable security safeguards can reach ₹250 crore. A failure to notify a breach can reach ₹200 crore, as can a breach of the children’s data duties. Significant Data Fiduciary breaches can reach ₹150 crore, and other breaches ₹50 crore. The Board weighs gravity, duration, repetition and mitigation.
These penalties fall on the fiduciary. A vendor’s exposure is mostly contractual, plus direct liability for any data it handles as a fiduciary itself.
Significant Data Fiduciaries
The government may notify some Data Fiduciaries as Significant Data Fiduciaries. Factors include data volume and sensitivity, and risk to people’s rights. They must appoint a Data Protection Officer based in India and an independent data auditor. Under Rule 13, they must run a Data Protection Impact Assessment and audit every 12 months and report key findings to the Board. They must also check that algorithmic software they use is not likely to pose a risk to people’s rights. Specified data may face limits on transfer outside India.
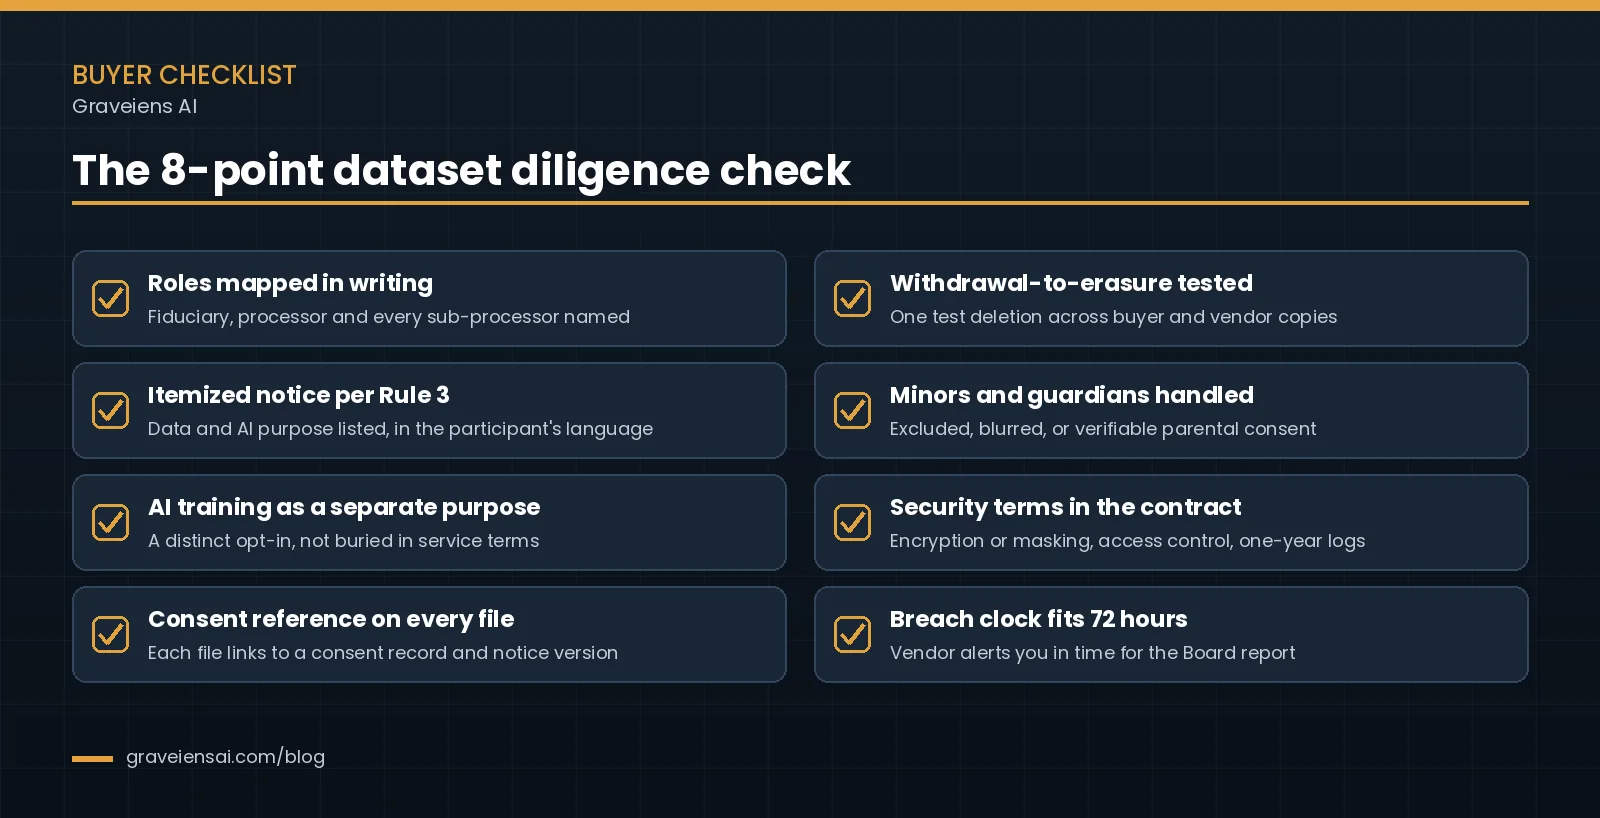
DPDP Act AI training data checklist: the 8‑point dataset diligence check
Use this check before a dataset enters your training pipeline. It works for new collections and for datasets you already hold. Each point maps to a clause above, so a “no” tells you exactly which gap to close.
- Roles mapped in writing. Name the fiduciary, the processor and every sub-processor for this dataset.
- Itemized notice per Rule 3. Lists the data collected and the AI training purpose, in the participant’s language.
- AI training as a separate purpose. A distinct opt-in, not a clause buried in service terms.
- Consent reference on every file. Each recording, clip or document links to a consent record and notice version.
- Withdrawal-to-erasure path tested. Run one test deletion across your copies and the vendor’s copies.
- Minors and guardians handled. Excluded, blurred, or covered by verifiable parental or guardian consent.
- Security terms in the contract. Encryption or masking, access control, and one-year logs per Rule 6.
- Breach clock that fits 72 hours. The vendor alerts you fast enough for your detailed Board report.
For scraped or third-party data, add two checks: provenance per source, and a written basis for any reliance on the public-data or research exemptions.
Want to run this check on a live project? Ask us for our consent & data-handling pack and compare it against your current vendor terms.
Common mistakes with personal data in training datasets
Most DPDP problems in AI data projects trace back to a few habits. Each one is cheap to fix before collection and expensive after.
- Reusing service consent for training. Consent covers the specified purpose only. A new model purpose needs its own notice and opt-in.
- Treating “public” as “free to use”. The exemption covers data the person made public, not everything a crawler can reach.
- Calling commercial training “research”. The research exemption fails if the data drives decisions about individuals.
- Stripping names and calling it anonymized. Voices, faces and rich metadata can still identify people.
- Forgetting bystanders and annotators. Both are Data Principals. Plan blurring or exclusion rules, and protect workforce records.
- Losing track of offshore access. Section 16 lets the government restrict transfers to notified countries. Keep a map of where data and annotators sit.
- No breach clock in the vendor contract. Without one, the 72-hour Board report is hard to meet.
Teams that already run an AI risk program can add these items to the data section of their register. A data validation pass before training is a natural place to catch them.
How Graveiens AI handles consent
We run explicit-consent data collection on every project. The workflow has four stages: participant onboarding, recording or capture management, metadata tagging and QA. Consent sits in the first stage, and nothing moves to capture without it.
- Consent first. Our consent-based data collection starts with participant onboarding, before any recording begins.
- Language coverage. We work in 25+ languages with deep Indic coverage. That matters when notices must be available in the language a participant speaks. See our voice and speech data services.
- Pay for approved deliverables. You review deliverables against agreed acceptance criteria and pay for what you approve.
- Quality system. Graveiens AI is ISO 9001 certified.
- Your terms, scoped together. Roles, notice wording, consent references in metadata, retention and deletion are project-specific. We scope them with you at kickoff.
If you want to see the output before you commit, our 30-minute speech sample set is free. For DPDP Act AI training data projects, we scope the role map and consent flow with you first.
Frequently asked questions
Does the DPDP Act apply to AI training data?
Yes, whenever the training data contains digital personal data about an identifiable person processed in India. That covers voice recordings, video with faces, names in text and identifying metadata. The Act’s definition of processing includes collection, structuring, storage, adaptation and use, so collection, annotation and training all fall in scope. Fully non-identifiable data falls outside it.
Can I train AI on publicly available personal data in India?
Only some of it. Section 3©(ii) excludes personal data that the person made public herself, or that someone was legally required to publish. Reposts, leaks and aggregator listings are not covered just because they are online. Commercial reuse for AI training is still debated, so record the source of each item and take legal advice before relying on the exemption.
Does the research exemption cover commercial AI model training?
Usually not on its own. Section 17(2)(b) exempts research, archiving or statistical processing only under two conditions. The data must not drive decisions about specific people, and the Second Schedule standards must be followed. Models that later drive decisions about individuals, such as credit or personalized offers, are a weak fit. Treat the exemption as narrow.
When do the DPDP consent rules take effect?
The notice rule (Rule 3) and the security, breach, children’s data and rights rules commence around 13 May 2027. That is eighteen months after the Rules were published on 13 November 2025. Consent manager registration (Rule 4) commences after twelve months, around 13 November 2026. As of October 2026, no Gazette amendment had shortened these windows.
Is a data annotation vendor a Data Fiduciary or a Data Processor?
Usually a Data Processor, because it processes personal data on the buyer’s behalf and instructions. The buyer decides purpose and means, so the buyer is the Data Fiduciary and stays responsible. A vendor becomes a fiduciary for data it uses for its own purposes, such as participant payment records. Write the role split into the contract.
Do I need a consent manager to collect speech data?
No. A consent manager under the DPDP Act is an option for the Data Principal, not a requirement for the buyer. A person may give, manage, review or withdraw consent through a registered Consent Manager. Consent manager DPDP registration opens around 13 November 2026. Your own notice, consent capture and records must still meet Sections 5 and 6 either way.
What are the penalties under the DPDP Act?
The Schedule sets maximums. Failing to take reasonable security safeguards can cost up to ₹250 crore. Failing to report a breach, or breaching the children’s data duties, can each cost up to ₹200 crore. Significant Data Fiduciary breaches can reach ₹150 crore, and other breaches up to ₹50 crore. The Board weighs gravity, duration and mitigation.
Ask for our consent & data-handling pack
Tell us what you are collecting, in which languages and for which model. We will share how we run consent, metadata and deletion on our projects, so you can check it against the 8‑point list above.
Ask us for our consent & data-handling pack. You can also request our free 30-minute speech sample set.
Sources
- Government of India, “The Digital Personal Data Protection Act, 2023 (No. 22 of 2023),” Gazette of India, 11 August 2023, via MeitY. meity.gov.in
- Ministry of Electronics and Information Technology, “Digital Personal Data Protection Rules, 2025,” G.S.R. 846(E), 13 November 2025. meity.gov.in
- Press Information Bureau, “DPDP Rules, 2025 Notified: A Citizen-Centric Framework for Privacy Protection and Responsible Data Use,” 17 November 2025. pib.gov.in
- Aashish Aryan, “Meity may cut compliance timeline for key DPDP rules to 12 months,” Business Standard, 22 January 2026. business-standard.com
About the author
Graveiens AI Editorial Team. The Graveiens AI editorial team writes about human data for AI: speech and egocentric data collection, annotation, validation and evaluation. Our guides draw on how we scope, capture and review consent-based data programs for AI teams.
Jitendra Choubay is the CEO & Founder of Graveiens AI, leading a human-in-the-loop data services team that helps AI builders with data collection, annotation, consent-backed voice data, transcription and LLM fine-tuning. He writes on building better, ethically sourced AI training data.
Get the next Graveiens AI article
Expert notes on AI data, annotation, LLMs and eLearning — no spam, unsubscribe anytime.
Need AI Development? Data Annotation? eLearning?
Talk to Graveiens AI about data collection, annotation, voice data, RLHF/SFT, LLM evaluation and AI training data — invoiced only on approved work.
Contact Graveiens AI